Chip-and-PIN in VISA USA relaxes PCI DSS requirements


Seen in SC Magazine

Author: Dan Kaplan

February 10, 2011

New Visa program could grow momentum for chip-and-PIN

A new Visa program that will exempt some European merchants from having to adhere to payment card security standards may spur the adoption of chip-and-PIN technology in the United States, according to a security analyst.

The program, announced Wednesday, 9-feb2011, eliminates the requirement for non-U.S. merchants to annually validate their compliance with the Payment Card Industry Data Security Standard (PCI DSS) if at least 75 percent of their Visa transactions originate from chip-enabled terminals.

The merchant would still be obligated to prove PCI compliance in relation to other transactions, such as MasterCard.

«I predicted this,» Avivah Litan, vice president and distinguished analyst at Gartner, told SCMagazineUS.com this week. «As payment card technology gets more secure, then there’s less of a need to secure the merchant sites. It’s redundant. Just secure the payment systems.»

To qualify, retailers must outfit their locations with terminals that accept «contact or dual contact and contactless» chips, according to Visa.

EMV, more commonly referred to as chip-and-PIN, is a payment technology largely used in the U.K., Spain, France, Germany  and in other european countries. It involves recognizing unique microchips embedded in credit and debit cards to validate that they are legitimate, and it has been credited with the declining fraud rates overseas.

Some firms in the United States, including mighty Walmart, are exploring the benefits of the technology, which has been held up here largely because of costs and incentive.

But the new Visa program may encourage more U.S. merchants to swap out their existing card readers if that means they too would be able to avoid the cost of PCI compliance.

«This may push the U.S. into it,» Litan said. «Now it’s a business case for merchants to start taking chip cards. It’s a good incentive.»

In October, the PCI Security Security Standards Council, tasked with managing the PCI DSS, released aguidance document for those organizations considering migrating their terminals to EMV.

Of course, for EMV to become a reality in the United States, banks must be willing to issue new cards containing chips. Yet, according to Visa, new debit card regulations that would cap the amount that card issuers can charge merchants when cards are swiped may curtail’ banks interest  – even though financial institutions, not merchants, are typically the ones that must reimburse consumers for incidents of fraud.

A recent study from the Boston Consulting Group estimated that card issuers could be on the hook for $25 billion in annual costs due to these stricter regulations, known as the Durbin Amendment because it is principally sponsored by Democratic Sen. Richard Durbin of Illinois.

“With such a dramatic potential for revenue loss, financial institutions will likely curtail investments in future innovations,» said Bill Sheedy, Visa’s group executive for the Americas.

Doug Johson, vice president of risk management policy the American Bankers Association (ABA), an industry trade group, agreed with Sheedy’s assessment.

«It demonstrates once again the folly and unintended consquences to mandate price controls within any environment,» Johnson told SCMagazineUS.com on Thursday.

That is not to say, though, that the ABA is opposed to EMV, said Johnson, adding that the association supports the development of security technology and is closely monitoring retail adoption of chip-enabled terminals.

«It’s not under our control to force,» said Johnson, who predicted that market forces may «leapfrog» EMV altogether and embrace some other technology, such as a cell phone payment system.

Johnson said that while banks would stand to save on some fraud-related reimbursements if EMV were to gain steam, illegal activity would still persist.

«All we’re doing is moving the fraud to somewhere where EMV is not in place, and we still take the loss,» he said.
e-invoicing: Huge Growth Predicted In Europe


As seen in Purchasing Insight.

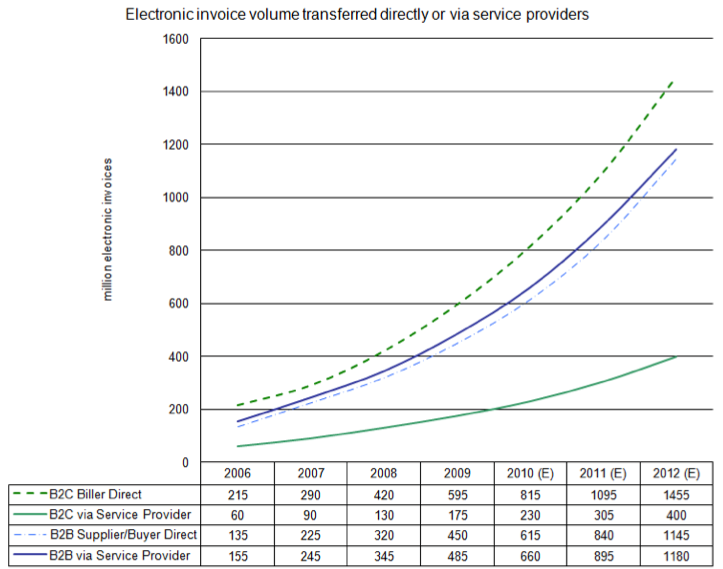
There is plenty of anecdotal evidence that 2011 is a big year for e-invoicing. Some new research published by Billentis reveals the scale of the anticipated growth in Europe.

Strong growth in e-invoicing predicted (Source: Billentis)

Strong growth in e-invoicing predicted (Source: Billentis)

Both in the business-to-business (B2B) and business-to-consumer (B2C) spaces, exponential growth is predicted in 2011 and 2012. e-invoicing between businesses will grow from a relatively modest 915 million in 2009 to nearly 2.5 billion in 2012 according to the Billentis research.

Consolidation in the e-invoicing market

The provider market is also likely to grow. According to Billentis, mergers and acquisition with grow from 14 in 2010 to 25 in 2011 with major consolidation expected if the market penetration of e-invoicing passes 15%

Visa adquirirá la compañía PlaySpan


Visa ha anunciado recientemente que ha llegado a un acuerdo para adquirir la compañía PlaySpan, una plataforma de pagos que se encarga de manejar transacciones sobre bienes digitales para juegos online, medios web, redes sociales  y en general ventas por Internet. La cifra de la transacción es de 190 millones de dólares.

Esta adquisición complementa la compra de CyberSource en el año 2010 consolidando el papel de Visa en el comercio electrónico tanto en el ámbito convencionalcomo en el móvil.

Se estima que en 2010 las ventas de comercio electrónico a nivel mundial ascendieron a 948 mil millones de dólares mientras la crisis ha hecho disminuir o estancarse las transacciones presenciales.  Mientras tanto PlaySpan se ha consolidado como líder en el comercio de bienes digitales, un segmento que ronda los 25.000 millones de dólares  a nivel mundial durante el 2010  y con espectativas de alcanzar los 280.000 millones de dólares en 2013.

PlaySpan ofrece la posibilidad de comprar créditos o monedas virtuales en línea a través de diferentes métodos como Paypal, DineroMail, ToditoCash, Wallie-card y Ultimate Points. También ofrece su “Ultimate Game Card” através de 20.000 distribuidores (incluyendo 7-Eleven, Wal-Mart, Blockbuster y Rite-Aid).

Entre las distribuidoras de videojuegos que ofrecen bienes virtuales se encuentra EverQuest, EVE Online, y todos los juegos de EA entre otros, sin mencionar que también se pueden comprar créditos para Farmville.

PlaySpan fundada en 2006 tiene su sede en Santa Clara, California y espera que su adquisición culmine este año durante el segundo trimestre fiscal de Visa.

Noticia de: Visa to Acquire PlaySpan (Playspan – PDF)

XML Cryptographic Security and Suite B


Several years ago, on 25 sept 2007, Sue A. Roddy (NSA), presented the article «XML Cryptographic Security and Suite B» in the XML Security Futures Workshop, urging the industry to develop Eliptic Curve Cryptography solutions that could be used commercially and also by government agencies.

This is the Article:

Background:

The Department of Defense (DOD) through the leadership of the Defense Information Security Agency (DISA) is pushing forward to use the Extensible Markup Language (XML) as a key element of the DOD information sharing effort. The National Security Agency (NSA), in support of the DOD, is interested in seeing XML security evolve in a manner that provides extensive interoperability between XML systems and use cryptographic mechanisms that meet the stringent security requirements of the DOD.

The NSA has established a suite of cryptographic algorithms, drawn from published standards established by the National Institute for Standards and Technology (NIST), as a primary basis for DOD cryptographic security in the 21st century. This suite of algorithms has come to be called, “SUITE B.” To promote interoperability among DOD elements and to maximize the DOD’s ability to utilize commercial technology in satisfying their mission, NSA encourages all commercial vendors to incorporate Suite B in their products. In particular NSA would like to see XML standards emerge which support the use of Suite B.

Suite B Defined

The sustained and rapid advance of information technology in the 21st century dictates the adoption of a flexible and adaptable cryptographic strategy for protecting national security information. Several years ago, the Committee for National Security Systems (CNSS) issued a policy stating that the Advanced Encryption Standard (AES) could be used to protect both classified and unclassified National Security information. However, because a single encryption algorithm could not satisfy all of the needs of the national security community, NSA created a larger set of cryptographic algorithms which could be used along with AES in the systems used by the DOD and other national security users. The NSA announced Suite B at the 2005 RSA Conference.

In addition to the AES, Suite B includes cryptographic algorithms for hashing, digital signatures, and key exchange. The entire suite of cryptographic algorithms is intended to protect both classified and unclassified national security systems and information. Because Suite B is also a subset of the cryptographic algorithms approved by NIST, Suite B is also suitable for use throughout the U.S. government. NSA’s goal in presenting Suite B is to provide industry with a common set of cryptographic
algorithms that they can use to create products that meet the needs of the widest range of US Government (USG) needs.

However, Suite B only specifies the cryptographic algorithms to be used. Many other factors need to be addressed in determining whether a particular device implementing a particular set of cryptographic algorithms should be used to satisfy a particular requirement.

Today SUITE B includes:

The original policy on AES use states that AES with either 128 or 256-bit keys are sufficient to protect classified information up to the SECRET level. In addition, other controls on manufacture, handling and keying are anticipated. These same key sizes are suitable for protecting both national security and non-national security related information throughout the USG.

Consistent with this policy, Elliptic Curve Public Key Cryptography using the 256-bit prime modulus elliptic curve as specified in FIPS-186-2 and SHA-256 are appropriate for protecting classified information up to the SECRET level. Use of both the 384-bit prime modulus elliptic curve and SHA-384 is necessary for the protection of TOP SECRET information.

Intellectual Property on Suite B:

Associated with most cryptographic algorithms, even those found in standards, are patents on various ways of implementing the cryptography in particularly efficient or novel ways. Although there are some particular implementations of both the advanced Encryption Systems and Secure Hash Algorithm that are patented, the basic algorithms are available worldwide for royalty free use.

Another key aspect of Suite B is its use of elliptic curve technology instead of classical public key technology. NSA has determined that rather than increase key sizes beyond today’s current 1024-bits, a switch to elliptic curve technology is warranted.

Like the AES and SHA there are no fundamental patents on elliptic curve cryptography, however, there are a number of
patents covering various aspects of elliptic curve technology and implementations. Certicom, the largest holder of elliptic curve patents, states on their company website that licensing their patents is not necessary for implementing elliptic curve cryptography. Rather, they state that they have patents on what they believe to be some of the “best ways to implement elliptic curve cryptography (ECC).”

In order to facilitate adoption of Suite B by industry, NSA has licensed the rights to 26 patents held by Certicom Inc. covering a variety of elliptic curve technology. Under the license, NSA has a right to sublicense vendors building equipment or components in support of US national security interests. While NSA offers vendors royalty free licenses for the use of these patents, NSA is not suggesting that licensing any of these patents or any other patents is necessary for implementing Suite B.

Conclusion:

To master the information space, DOD and the IC need to be able to share, analyze and secure vast amounts of information. In order to prevent all of the information in DOD networks from becoming a meaningless tower of babel, standards such as XML are critical. NSA would like to see security for XML evolve in a manner that supports the DOD’s need for secure information sharing. To that end, NSA would like to see the adoption of Suite B cryptography as a security option for XML.

Inseguridad jurídica en la energía fotovoltáica


Un estado de derecho se debe de caracterizar por la seguridad jurídica. Si las disposiciones que aparecen en el BOE se modifican cada dos por tres sin necesidad aparente, se demuestra en cada modificacion que las normas que se cambian estaban mal en primer lugar. Pero es que además, cuando afecta a decisiones económicas, cada cambio es un cambio de reglas de juego en mitad de la partida. El dislate llega al máximo cuando se imponen modificaciones con efectos retroactivos.

Esto es lo que ha pasado en el mundo de la energía fotovoltáica, y que ha dado lugar a la movilización de los afectados por la nueva normativa de placas fotovoltaicas.

La situación se resume muy bien en el artículo las consecuencias e implicaciones del RD-Ley 14/2010 del bufete Navas & Cusí Abogados que reproduzco:

Las consecuencias e implicaciones del RD-Ley 14/2010

En el año 2007, el Gobierno español incentivó y fomentó el uso, producción y venta de energías renovables alternativas, fomentando especialmente la inversión en plantas fotovoltaicas de energía eléctrica. Para ello, aprobó el Real Decreto 661/2007 mediante el cual se incentivó la colocación de plantas fotovoltaicas asegurando la inversión
realizada estipulando un precio fijo por el que las compañías eléctricas compraban la totalidad de la energía eléctrica generada por dichas placas fotovoltaicas.

Ante la garantía y seguridad ofrecida por el Estado, cientos de personas invirtieron sus ahorros en la instalación de plantas
fotovoltaicas, tanto por estar en la creencia de que el gobierno deseaba crear una auténtica fuente eficaz de energía alternativa, como por la seguridad que otorga contratar con el Estado.

El pasado viernes 24 de Diciembre de 2010 se publicó en el BOE el Real Decreto-Ley 14/2010 mediante el cual el gobierno, de forma unilateral y sin consultar a los afectados e interesados del sector, aplica medidas económicas con carácter retroactivo que afectan a todos los inversores con plantas fotovoltaicas, sin diferenciar entre los productores hasta la actualidad y los nuevos productores con posterioridad al Decreto,  limitando las horas de producción eléctrica e instaurando un peaje transitorio de acceso a las redes de transporte y distribución a satisfacer por los productores de energía eléctrica.

En resumen:

  • Los propietarios de plantas fotovoltaicas estarán obligados, a partir del 1 de enero de 2011 y hasta que no se desarrolle un reglamento que imponga otros precios, a pagar un peaje de acceso por distribuir la energía eléctrica de 0,5 €/MWh.
  • Se procede a limitar las horas de funcionamiento de las instalaciones fotovoltaicas hasta el 31 de Diciembre de 2013. Las limitaciones para las instalaciones fotovoltaicas reguladas por el Real Decreto 661/2007 serán los siguientes, según su tecnología:
> Instalación fija: 1.250 horas equivalentes de referencia / año
> Instalación con seguimiento a 1 eje: 1.644 horas equivalentes de referencia / año
> Instalación con seguimiento a 2 ejes: 1.707 horas equivalentes de referencia / año

El presente Real Decreto comportará grandes perjuicios y pérdidas económicas a los inversores, quienes decidieron realizar la inversión amparados en unas determinadas condiciones que actualmente el Gobierno ha  modificado de forma unilateral y sin respetar las condiciones contractuales pactadas, dado que no podrán recuperar la inversión realizada en el tiempo estimado por limitar el Gobierno la producción de energía eléctrica y dejar de pagar los importes y los KW estimados.

Dicho Real Decreto y sus disposiciones transitorias pueden afectar a principios constitucionales básicos como son la seguridad jurídica, la responsabilidad y la interdicción de la arbitrariedad de los poderes.

Certificados duales RSA – ECC (enmarcados en el ENS)


EADTrust ha iniciado una campaña de promoción de certificados electrónicos según un nuevo modelo. En vez de entregar un solo certificado, entrega dos. El primer certificado, RSA, con clave de 2048 bits puede ser utilizado de forma convencional, en servidores SSL. El segundo (vinculado con el primero por una regla de generación cruzada) cumple los principos Binum. Es un certificado ECC con clave de 256 bits (robustez equivalente a 3070 bits en claves RSA) y se utiliza también en servidores SSL.

Los certificados se entregan en formato PKCS#12 y la generación de claves (llevada a cabo por EADTrust) verifica las recomendaciones contra los ataques matemáticos identificados en la literatura académica. Los certificados tienen una duración de 3 años, por lo que requieren menos esfuerzo de gestión (que los certificados anuales). El precio de los certificados (de cada pareja) es de 99 euros si identifican un dominio y 199 euros en el caso de pareja de certificados multidominio (*). Hasta el 30 de junio de 2011, el coste de cada pareja de certificados será de 50 y 100 euros respectivamente.

Dado que los certificados ECC no los soportan todos los navegadores, ayudamos a las entidades solicitantes a configurar los servidores de forma que se usen los algoritmos más potentes que soporte cada navegador, combinando ambos certificados.

Compruebe si su navegador soporta ambas tecnologías instalando los certificados raíz de las dos jerarquías de certificación:

El uso de claves largas en RSA (al menos de 2048 bits) y el empleo de algoritmos ECC como ECDSA son algunos de los aspectos recomendados por el CCN (Centro Criptológico Nacional) en la documentación de seguridad relativa a la implantación del Esquema Nacional de Seguridad. En particular, el documento Guía 807 – Criptología de empleo en el Esquema Nacional de Seguridad estudia los diferentes alguritmos y sus ataques conocidos y hace recomendaciones sobre los más adecuados en función del objetivo perseguido (identificación, autenticación, cifrado, firma, confidencialidad en SSL,…)

También hay recomendaciones equivalente en los documentos de la administración nortemaericana NIST (National Institute of Standards and Technology) FIPS (Federal Information Processing Standards) 186 -2 y FIPS 186-3 respectivamente en los apéndices 6 y D en las secciones Recommended Elliptic Curves for Federal Government use (United States).

A nivel europeo, las especificaciones que tratan sobre los algoritmos criptográficos que se usan para firma electrónica (por ejemplo) se describen en el documento ETSI TS 102 176-1 V2.0.0 (2007-11) “Technical Specification. Electronic Signatures and Infrastructures (ESI); Algorithms and Parameters for Secure Electronic Signatures; Part 1: Hash functions and asymmetric algorithms».

Otras normas aplicables:

  • RFC 3278 «Use of Elliptic Curve Cryptography (ECC) Algorithms in Cryptographic Message Syntax (CMS)»
  • RFC 4050 «Using the Elliptic Curve Signature Algorithm (ECDSA) for XML Digital Signatures»
  • RFC 4051 “Additional XML Security Uniform Resource Identifiers (URIs)”
  • RFC 4492 “Elliptic Curve Cryptography (ECC) Cipher Suites for Transport Layer Security (TLS)”
  • ISO/IEC 15946 “Information technology — Security techniques — Cryptographic techniques based on elliptic curves”
  • ANSI X9.62:2005 “Public Key Cryptography for the Financial Services Industry, The Elliptic Curve Digital Signature Algorithm (ECDSA)”

Otras referencias a EADTrust en este Blog:

Actualización: A partir de 2020, solo se entrega el certificado solicitado. Las peticiones de certificado deben incluir el tipo de criptotografía deseado, que puede llegar a 8192 bits de tamaño en RSA y 384 bits en ECC.

Mejoras en el soporte de OpenSC para el DNIe en Linux y Mac,


Muy buenas noticias estos dias para el DNIe y la posibilidad de usarlo en algunas plataformas en las que era un poco más complicado.

Primero, un aplauso para Jonsy Gaviota (Juan Antonio Martínez – EB4GPE) y su trabajo OpenDNI.

Segundo la Compilación de OpenDNIe para Mac OS X del Blog Cajón de sastre de Kounch

Gracias por vuestro esfuerzo.

CIR Technical Working Group


The EMV standards developed and maintained by EMVCo are the technical basis for card-based payment systems in many countries. The CIR (Common Implementation Recommendations) Technical Working Group is an open standardisation initiative of EMV implementers in Europe and acts as the technical reference group for the European EMV Users Group and the European members of the EMVCo Board of Advisors. The CIR Technical Working Group is not meant to duplicate any efforts at EMVCo level, but to complement the work at EMVCo by the input of technical experts who are actively involved in the deployment of the EMV specifications.

Participants of the CIR Technical Working Group are

The CIR Technical Working Group is supported by the observers

The aim of the CIR Technical Working Group is to come to harmonised technical specifications for EMV implementations for any card-based payment system. The work is not intended to change the EMV specifications but to fill in the «grey areas» of the EMV specifications and to reduce both the effort necessary to implement cards and terminals as well as the number of different implementations, thus allowing for less expensive devices.

The work of the CIR Technical Working Group started in 2003 with the objective of harmonising EMV implementations on cards. Based on this preparatory work, and with the support of the CIR Technical Working Group, EMVCo set up the Common Core Working Group (CCWG) which produced the EMVCo Common Core Definitions (CCD) and the EMVCo Common Payment Application (CPA) Specification, which allow a common EMV implementation on cards for all payment systems.

As a next step, the CIR Technical Working Group, in coordination with the European EMV Users Group, produced a set of common implementation recommendations for terminals, in the form of detailed flow charts describing the terminal behaviour, to clarify and enhance the EMV specifications and to improve interoperability. These Common Implementation Recommendations for Terminals have been reviewed with EMVCo and are the basis for the current work of the CIR Technical Working Group on a detailed terminal specification.

Starting in 2007, the CIR Technical Working Group has been working for the European Payments Council (EPC) Cards Working Group as Identified Initiative for the Card-to-Terminal and Cardholder-to-Terminal standardisation domains. The Functional Requirements in the European Payments Council (EPC), SEPA Cards Standardisation «Volume» are based on the input of the CIR Technical Working Group.

The CIR Technical Working Group works in close cooperation with other standardisation initiatives, such as EPAS, which concentrates on the Terminal-to-Acquirer interfaces, and CAS, which concentrates on the requirements for mutual recognition of certifications.

Los 902 y sus equivalentes de teléfono fijo (actualización a octubre de 2026)


Si una empresa te ofrece un teléfono que empieza por 902 para atenderte, tienes derecho a que te dé también un número que no te cueste más que una llamada normal a un fijo o a un móvil. Hoy la ley lo exige, y desde finales de 2026 las grandes empresas tendrán además nuevas obligaciones de atención al cliente.

Nota de actualización (octubre de 2026). Publiqué esta entrada en febrero de 2011 con una lista de equivalencias entre números 902 y fijos geográficos, cuando la única forma de evitar el sobrecoste era buscar el número alternativo por tu cuenta. Sigue siendo una de las más leídas del blog, y los lectores siguen preguntando en los comentarios por equivalencias concretas. Desde entonces la situación ha cambiado: la ley obliga ahora a ofrecer esa alternativa. He actualizado el contenido para explicar qué derechos tienes y cómo ejercerlos.

Qué son los 901 y 902 y por qué salen caros

Los 901 y 902 son números de red inteligente: no están ligados a una línea física, sino que la operadora los redirige al centro de atención que elija la empresa. Se popularizaron en los años noventa porque eran fáciles de recordar y, cuando las llamadas interprovinciales se cobraban caras, permitían llamar desde cualquier provincia a un precio único.

Con la llegada de las tarifas planas la situación se invirtió. Las llamadas a fijos y móviles están incluidas en casi todas las tarifas planas, pero los 901 y 902 suelen quedar fuera y se cobran aparte. En el 902 el coste lo paga íntegramente quien llama, y en el 901 se reparte con la empresa. El resultado era que llamar a un servicio de atención al cliente, a menudo con largas esperas, podía encarecer mucho la factura.

Qué dice hoy la ley

Desde 2020, para todas las empresas. El Real Decreto-ley 37/2020 modificó la Ley General para la Defensa de los Consumidores y Usuarios. Desde entonces:

  • Llamar a un teléfono de atención al cliente no puede costar más que una llamada a un fijo geográfico o a un móvil estándar.
  • Una empresa puede mantener su 902, pero debe ofrecer en igualdad de condiciones un número geográfico o móvil alternativo e informar de que existe.
  • Las empresas de servicios básicos (agua, gas, electricidad, servicios financieros y de seguros, postales, transportes, entre otros) deben ofrecer un teléfono gratuito.
  • Las líneas de atención al cliente no pueden usarse para hacer publicidad.

Desde diciembre de 2026, para las grandes empresas. La Ley 10/2025, de 26 de diciembre, de servicios de atención a la clientela entró en vigor el 28 de diciembre de 2025 y da a las empresas obligadas un plazo de adaptación de doce meses, hasta el 28 de diciembre de 2026. Se aplica a las que prestan servicios básicos de interés general (suministros, transporte, servicios postales, telecomunicaciones y servicios financieros), a las grandes empresas que venden a consumidores (250 o más trabajadores, o más de 50 millones de euros de facturación) y a la Administración General del Estado. Entre otras cosas:

  • Mantiene la regla del coste: no más que una llamada normal, con número alternativo si hay línea de tarificación especial.
  • Prohíbe desviar un número gratuito a otro que tenga coste.
  • El 95 % de las solicitudes de atención personalizada deben atenderse, de media, en menos de tres minutos, y la empresa no puede cortar la llamada por un tiempo de espera largo.
  • Tienes derecho a que te atienda una persona que se identifique. Los contestadores automáticos y los bots deben ofrecer siempre esa opción desde el menú principal.
  • Las quejas y reclamaciones deben resolverse en un máximo de 15 días hábiles, salvo que la normativa sectorial fije otro plazo.

Cómo encontrar el número alternativo

  1. Mira la sección de contacto de la web de la empresa. Si ofrece un 902, la ley la obliga a informar del número alternativo, normalmente junto a él.
  2. Revisa tus facturas, contratos y comunicaciones. Suele figurar en la letra pequeña o en el apartado de atención al cliente.
  3. Si llamas al 902, pide el número geográfico o móvil para la próxima vez. Tienes derecho a conocerlo.
  4. Comprueba tu tarifa. Algunas operadoras incluyen las llamadas a 902 en ciertas tarifas, y conviene saberlo antes de llamar.

Qué hacer si no te lo ofrecen

  • Pide la hoja de reclamaciones o presenta una reclamación por escrito ante la empresa, y guarda el justificante.
  • Si no se resuelve, acude a la oficina municipal de información al consumidor (OMIC) o al servicio de consumo de tu comunidad autónoma, que son quienes sancionan estos incumplimientos.
  • Si la empresa es una operadora de telecomunicaciones, puedes reclamar también ante la Oficina de Atención al Usuario de Telecomunicaciones.
  • Si ya te han cobrado una llamada a un 902 sin haberte ofrecido alternativa, inclúyelo en la reclamación con la fecha, la hora y la duración que aparecen en tu factura.

Sobre la lista de equivalencias de 2011

La versión original de esta entrada recogía una lista de equivalencias por sectores (bancos, seguros, telefonía, organismos oficiales…) tomada de otras webs. Quince años después, muchos de esos números han cambiado, algunas empresas han desaparecido o se han fusionado, y las webs de origen ya no están actualizadas. Por eso no la reproduzco: un número equivocado puede hacerte perder más tiempo que el propio 902. La vía fiable es la que exige la ley: el número alternativo que publica la propia empresa.

Fuentes

Si te ha resultado útil, quizá te interesen también…

En este blog escribo sobre confianza digital: firma electrónica, identidad digital, criptografía y su marco jurídico. Algunas entradas que pueden interesarte:

SMS de CardVISA (Ojo Phishing)


El phishing llega a los SMS.

El blog Histo-piniones cuenta en primera persona el caso.

Lo primero que hay que decir es que NUNCA hay que acceder a una supuesta entidad financiera haciendo click en un mensaje que nos llegue por correo electrónico, sino que hay que teclear directamente las URL de la página web de nuestra entidad financiera en caso de que tengamos alguna duda y pensaemos que un mensaje pueda tener algo de cierto.

En el caso de este phishing por SMS propone teclear como URL una página web denominada www.cardvisa.us que puede que a algunas personas les parezca como una dirección compatible con su tarjeta VISA.

Hay que decir que las entidades gestoras de medios de pago son relativamente «invisibles» en los procesos de gestión de pago con tarjeta, y que solo son visibles las entidades financieras del titular de la tarjeta (denominada entidad emisora) y la del comercio (denominada entidad adquirente). Así que ante cualquier duda, debemos contactar con NUESTRA ENTIDAD FINANCIERA.

Una posible excepción a esta recomendación se da con la posibilidad de reportar la pérdida o robo de varias tarjetas en una única llamada para bloquearlas de la forma más rápida posible.

En España, se puede llamar a estos números de teléfono en caso de emergencia:

  • 4b: 91 362 62 00 – 902 11 44 00 (Tarjetas VISA y MasterCard)
  • Servired: 902 19 21 00 – 91 519 21 00 (Tarjetas VISA y MasterCard)
  • Euro6000: 902 20 6000 – 91 596 53 35 (Tarjetas VISA y MasterCard)
  • American Express: +34 91 400 42 50 – 902 37 56 37
  • Dinner’s Club: 902 401 112 – 912 114 300

VISA Europe advierte en una de sus páginas sobre la forma de proceder ante mensajes de correo sospechosos, y concluye:

Si ha recibido un correo electrónico sospechoso o tiene dudas sobre la autenticidad de algún sitio web, contacte con la entidad financiera emisora de su tarjeta. También puede reenviar el correo sospechoso o la dirección URL del sitio web sobre el que tenga dudas a nuestra siguiente dirección de correo electrónico: phishing@visa.com.

También VISA Europe proporciona una lista de números en diversos paises en los que podemos consultar la forma de proceder en caso de pérdida o robo de nuestra tarjeta:

  • Alemania 0800-811-8440
  • Anguilla 1-800-847-2911
  • Antigua 1-800-847-2911
  • Arabia Saudita 1-800-10-866-654-0129
  • Argentina 0800-666-0171
  • Aruba 800-1518
  • Australia 1-800-125-440
  • Austria 0800-200-288 y después 800-892-8134
  • Bahamas 1-800-847-2911
  • Bahrein 8000-006
  • Barbados 1-800-847-2911
  • Bélgica 0800-1-8397
  • Bolivia 800-10-0188
  • Bonaire 001-800-847-2911
  • Bosnia Herzegovina 00-800-0010-888-557-4457
  • Brasil 0800-891-3680
  • Bulgaria 00-800-0010-888-557-4446
  • Canadá 1-800-847-2911
  • Chile 1230-020-2136
  • China (Norte) 10-800-711-2911
  • China (Sur) 10-800-110-2911
  • Colombia 01-800-912-5713
  • Corea 00798-11-908-8212
  • Costa Rica 0-800-011-0030
  • Croacia 0-800-220111-866-654-0125
  • Curaçao 001-800-847-2911
  • Dinamarca 80-010277
  • Dominica 1-800-847-2911
  • Egipto (excepto El Cairo) 02-510-0200-866-654-0128
  • Egipto (sólo El Cairo) 510-0200-866-654-0128
  • Emiratos Árabes Unidos 0-800-121-866-654-0112
  • Eslovaquia 0-800-000-101-800-406-9970
  • España 900-99-1124
  • Estados Unidos 1-800-847-2911
  • Estonia 800-12001-800-406-9982
  • Filipinas 1-800-1-111-9015
  • Finlandia 0800-11-0057
  • Francia 0800-90-1179
  • Gibraltar 8800-877-3745966
  • Granada 1-800-847-2911
  • Grecia 00-800-11-638-0304
  • Guam 1-800-847-2911
  • Guatemala 1-800-999-0115
  • Holanda 0800-022-3110
  • Hong Kong 800-96-7025
  • Hungría 06-800-17682
  • India No disponible
  • Indonesia 001-803-1-933-6294
  • Irlanda 1-800-55-8002
  • Islas Bermudas 1-800-847-2911
  • Islas Caimán 1-800-847-2911
  • Islas Turku y Caicos 0-1-800-847-2911
  • Islas Vírgenes Británicas 1-800-847-2911
  • Islas Vírgenes Estadounidenses 1-800-847-2911
  • Israel 1-800-941-1605
  • Italia 800-819-014
  • Jamaica 0-800-847-2911
  • Japón 00531-11-1555
  • Jordania 1-880-0000-888-557-4442
  • Kazajstán 8-800-121-4321-888-557-4447
  • Kenia 866-654-0162
  • Letonia 800-2131
  • Líbano (excepto Beirut) 01-426-801-866-654-0130
  • Líbano (sólo Beirut) 426-801-866-654-0130
  • Liechtenstein 0800-89-4732
  • Lituania 8-800-900-28-800-406-9962
  • Luxemburgo 0800-2012
  • Macedonia 99-800-4288-888-557-4458
  • Malasia 1800-80-0159
  • Marruecos 002-11-0011-866-654-0163
  • Mauricio 01-120-866-654-0165
  • México 001-800-847-2911
  • Mónaco No disponible
  • Montserrat 1-800-847-2911
  • Nevis 1-800-847-2911
  • Noruega 800-12052
  • Nueva Zelanda 0800-44-3019
  • Okinawa 00531-11-1555
  • Panamá 001-800-111-0016
  • Paraguay 008-11-800-800-599-1137
  • Perú 800-890-0623
  • Polonia 0-0-800-111-1569
  • Portugal 800-8-11-824
  • Puerto Rico 1-800-847-2911
  • Qatar 0800-011-77-888-557-4428
  • Reino Unido 0800-89-1725
  • República Chechenia 800-142-121
  • República Dominicana 1-800-847-2911
  • Rumania 021-800-4288-888-557-4416
  • Rusia (excepto Moscú/San Petersburgo) 8-10-800-110-1011-866-654-0164
  • Rusia (sólo Moscú) 755-5042-866-654-0164
  • Rusia (sólo San Petersburgo) 325-5042-866-654-0164
  • Saba 1-800-847-2911
  • Saint Eustatius 1-800-847-2911
  • San Marino 800-819-014
  • San Martín 1-800-847-2911
  • Senegal 810-3072-888-557-4451
  • Singapur 800-110-0344
  • St. Kitts/Nevis 1-800-847-2911
  • Sudáfrica 0800-990-475
  • Suecia 020-795-675
  • Suiza 0800-89-4732
  • Tailandia 001-800-11-535-0660
  • Taiwán 00801-10-3008
  • Trinidad y Tobago 1-800-847-2911
  • Turquía 00-800-13-535-0900
  • Ucrania 8-100-11-888-557-4445
  • Uruguay 00-0411-940-7915
  • Venezuela 0800-1-002167

También Mastercard ofrece una lista de contactos internacionales:

  • Asia / Pacific
  • American Samoa: 1-1-800-307-7309
  • Australia: 1800-120-113
  • China: 10-800-110-7309
  • Guam: 1-800-307-7309
  • Hong Kong: 800-966677
  • India: 000-800-100-1087
  • Indonesia: 001803-1-887-0623
  • Japan: 00531-11-3886
  • Korea: 0079-811-887-0823
  • Malaysia: 1-800-804594
  • New Zealand: 0800-44-9140
  • Philippines: 1-800-1-111-0061
  • Saipan: 1-800-307-7309
  • Singapore: 800-1100-113
  • Taiwan: 00801-10-3400
  • Thailand: 001-800-11-887-0663Europe
  • Austria: 0800-21-8235
  • Belgium: 001-800-307-7309
  • Czech Republic: 800-142-494
  • Denmark: 8001-6098
  • Finland: 08001-156234
  • France: 0-800-90-1387
  • Germany: 0800-819-1040
  • Greece: 00-800-11-887-0303
  • Hungary: 06800-12517
  • Ireland: 1-800-55-7378
  • Italy: 800-870-866
  • Liechtenstein: 0800-89-7092
  • Luxembourg: 800-2-4533
  • Monaco: 0-800-90-1387
  • Montserrat: 1-800-307-7309
  • Netherlands: 0800-022-5821
  • Norway: 800-12697
  • Poland: 0-0800-111-1211
  • Portugal: 800-8-11-272
  • San Marino: 800-870-866
  • Spain: 900-97-1231
  • Sweden: 020-791-324
  • Switzerland: 0800-89-7092
    Turkey: 00-800-13-887-0903
  • United Kingdom: 0800-96-4767
  • Vatican City State: 800-870-866Latin America / Caribbean
  • Anguilla: 1-800-307-7309
  • Antigua and Barbuda: 1-800-307-7309
  • Argentina: 0800-555-0507
  • Bahamas: 1-800-307-7309
  • Barbados: 1-800-307-7309
  • Bermuda: 1-800-307-7309
  • Bolivia: 800-10-0172
  • Bonaire: 001-800-307-7309
  • Brazil: 0800-891-3294
  • Cayman Islands: 1-800-307-7309
  • Chile: 1230-020-2012
  • Colombia: 01-800-912-1303
  • Costa Rica: 0-800-011-0184
  • Curacao: 001-800-307-7309
  • Dominica: 1-800-307-7309
  • Dominican Republic: 1-800-307-7309
  • Grenada: 1-800-307-7309
  • Guatemala: 1-800-999-1480
  • Jamaica: 0800-307-7309
  • Mexico: 001-800-307-7309
  • Panama: 001-800-307-7309
  • Peru: 0-800-307-7309
  • Puerto Rico: 1-800-307-7309
  • Saba: 1-800-307-7309
  • St. Eustatius: 1-800-307-7309
  • St. Kitts-nevis: 1-800-307-7309
  • St. Maarten: 1-800-307-7309
  • Trinidad and Tobago: 1-800-307-7309
  • Turks and Caicos Islands: 01-800-307-7309
  • Venezuela: 0800-1-002902
  • Virgin Islands, British: 1-800-307-7309
  • Virgin Islands, U.S.: 1-800-307-7309Middle East / Africa
  • Bahrain: 8000-0087
  • Cyprus: 080-90569
  • Israel: 180-941-8873
  • South Africa: 0800-990418US / Canada
  • Canada: 1-800-307-7309
  • United States: 1-636-722-7111